What this guidebook covers
Every customer a dealership serves leaves personal data behind: IDs, contact details, finance papers and service history. The PDPL's grace period ended on 14 September 2024, and on 16 January 2026 SDAIA announced 48 decisions confirming violations, naming four recurring failures: no legal basis, unjustified disclosure, weak security and marketing without consent.
This guidebook covers 12 PDPL standards with 29 checkpoints, from privacy notices and consent records to processing records, breach notification, data subject requests, processor contracts, cross-border transfers and the physical security of customer files.
The 12 PDPL standards
| Code | Standard | Ideal fix time |
|---|---|---|
| DAT-001 | PDPL awareness materials displayed | 7 days |
| DAT-002 | Privacy notice at collection points | 72 hours |
| DAT-003 | Lawful basis and consent records | 7 days |
| DAT-004 | Marketing SMS and email consent | 24 hours |
| DAT-005 | Records of processing activities | 30 days |
| DAT-006 | DPO appointment and SDAIA registration | 30 days |
| DAT-007 | Data retention and destruction | 30 days |
| DAT-008 | Personal data breach notification | 7 days |
| DAT-009 | Data subject request handling | 7 days |
| DAT-010 | Data processor contracts | 30 days |
| DAT-011 | Cross-border data transfers | 30 days |
| DAT-012 | Physical security of customer files | Immediate |
How to run a PDPL compliance audit, step by step
- Confirm what applies. Map where the site collects personal data (showroom, service reception, finance desk, website, CRM) and which vendors receive it.
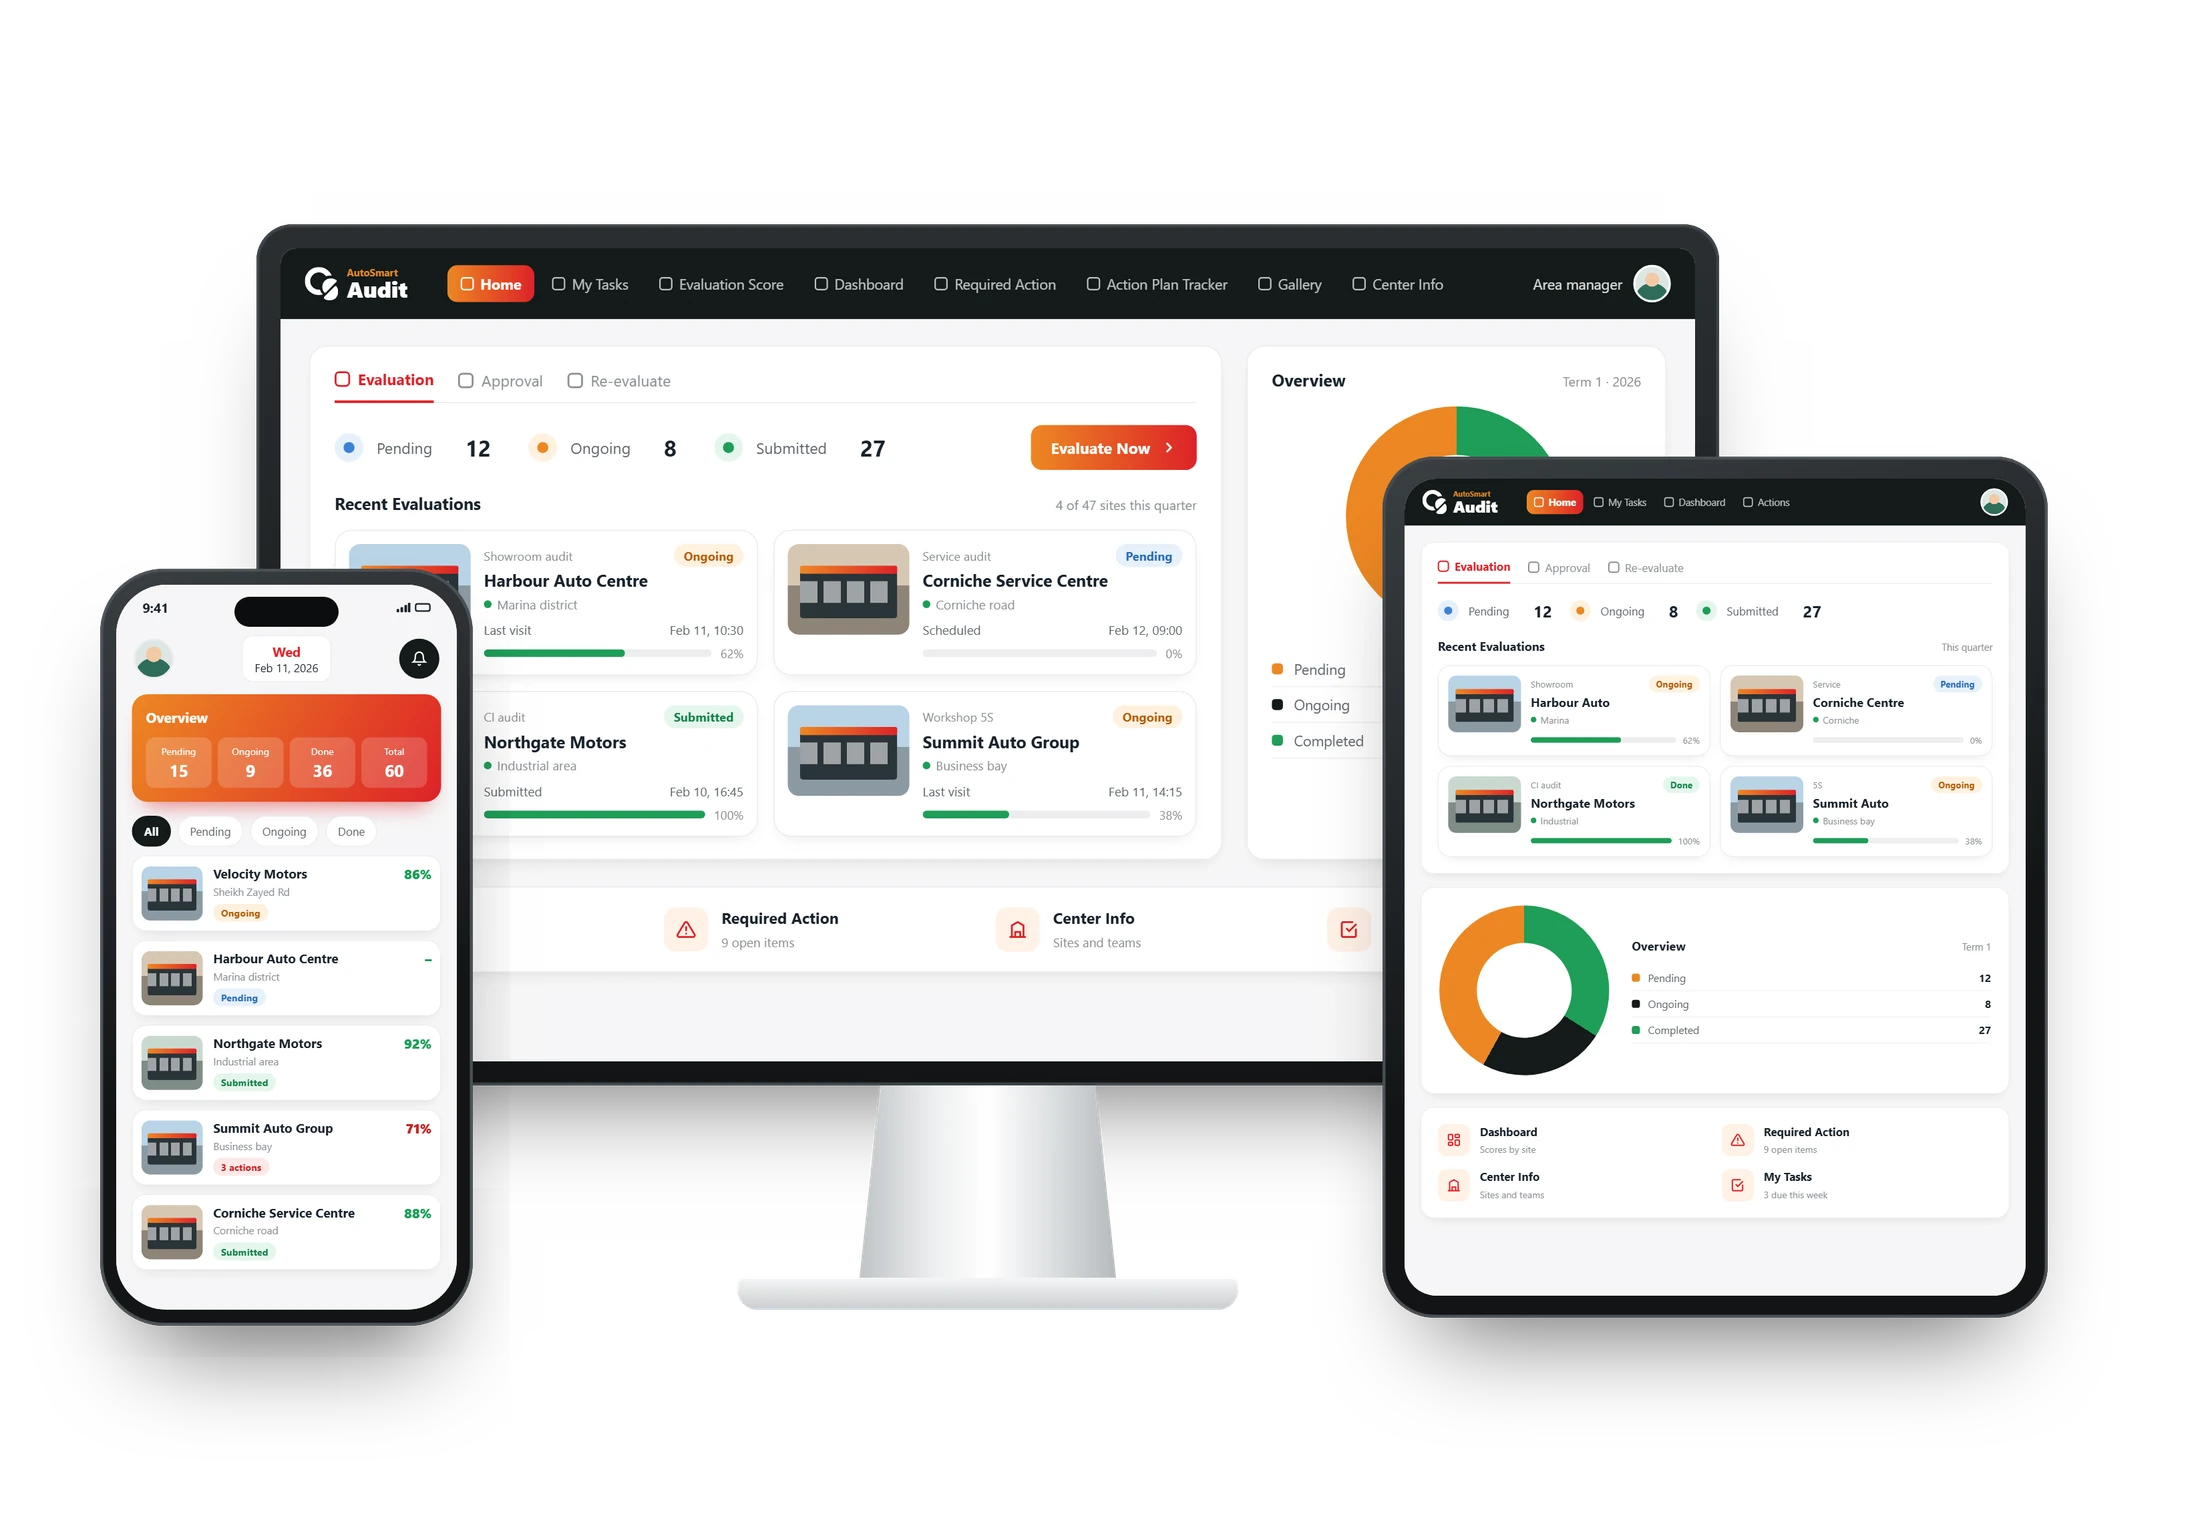
- Walk the site, standard by standard. Score each of the 29 checkpoints Pass, Fail or N/A. N/A only where the standard rules it out, with the reason recorded. Sample deal files and marketing lists, and check each has a lawful basis or consent record.
- Capture the evidence. A pass counts only with proof captured at the time of the audit: the privacy notice at each collection point, consent records, the processing register, processor contracts and photos of where files are kept.
- Give every fail an owner and a fix time. Record what you saw and who owns the fix. Each standard carries an ideal fix time, from immediate to 30 days, counted from audit submission (see the table above).
- Fix it, then prove it. The site fixes the cause and uploads proof of closure; the auditor checks the proof before closing the finding.
- Re-check at the next audit. Confirm closed findings stay closed, and look for the same fail at your other sites so one gap doesn't repeat across the network.
Who this guidebook is for
- Dealer principals
- Data protection officers
- Compliance officers
- Auditors
A reference document, not legal advice. Fines and rules change: check the current text with the regulator or your legal adviser before acting.