What this guidebook covers
A dealer holds more data than many banks: ID cards, driving licences, bank details, addresses and vehicle data, passed on to the importer, banks and insurers. GDPR (RODO in Polish) allows fines of up to €20 million or 4% of worldwide turnover. UODO (the Personal Data Protection Office) fined McDonald's Polska PLN 16.9 million over gaps in its risk analysis and security.
This guidebook covers 5 data protection standards for dealers, with 12 checkpoints: marketing consent, the information clause, customer rights requests, data security with breach reporting within 72 hours, and processing agreements and retention. The guidebook PDF is in Polish.
The 5 data protection standards
| Code | Standard | Ideal fix time |
|---|---|---|
| DAN-01 | Marketing consent | Immediate |
| DAN-02 | Information clause | 30 days |
| DAN-03 | Customer rights requests | 7 days |
| DAN-04 | Data security | 24 hours |
| DAN-05 | Processing agreements and retention | 30 days |
How to run a Polish GDPR (RODO) data protection audit, step by step
- Confirm what applies. Map every channel where customer data is collected and everyone it is passed to; data sent to the importer needs a legal basis and must be described in the information clause.
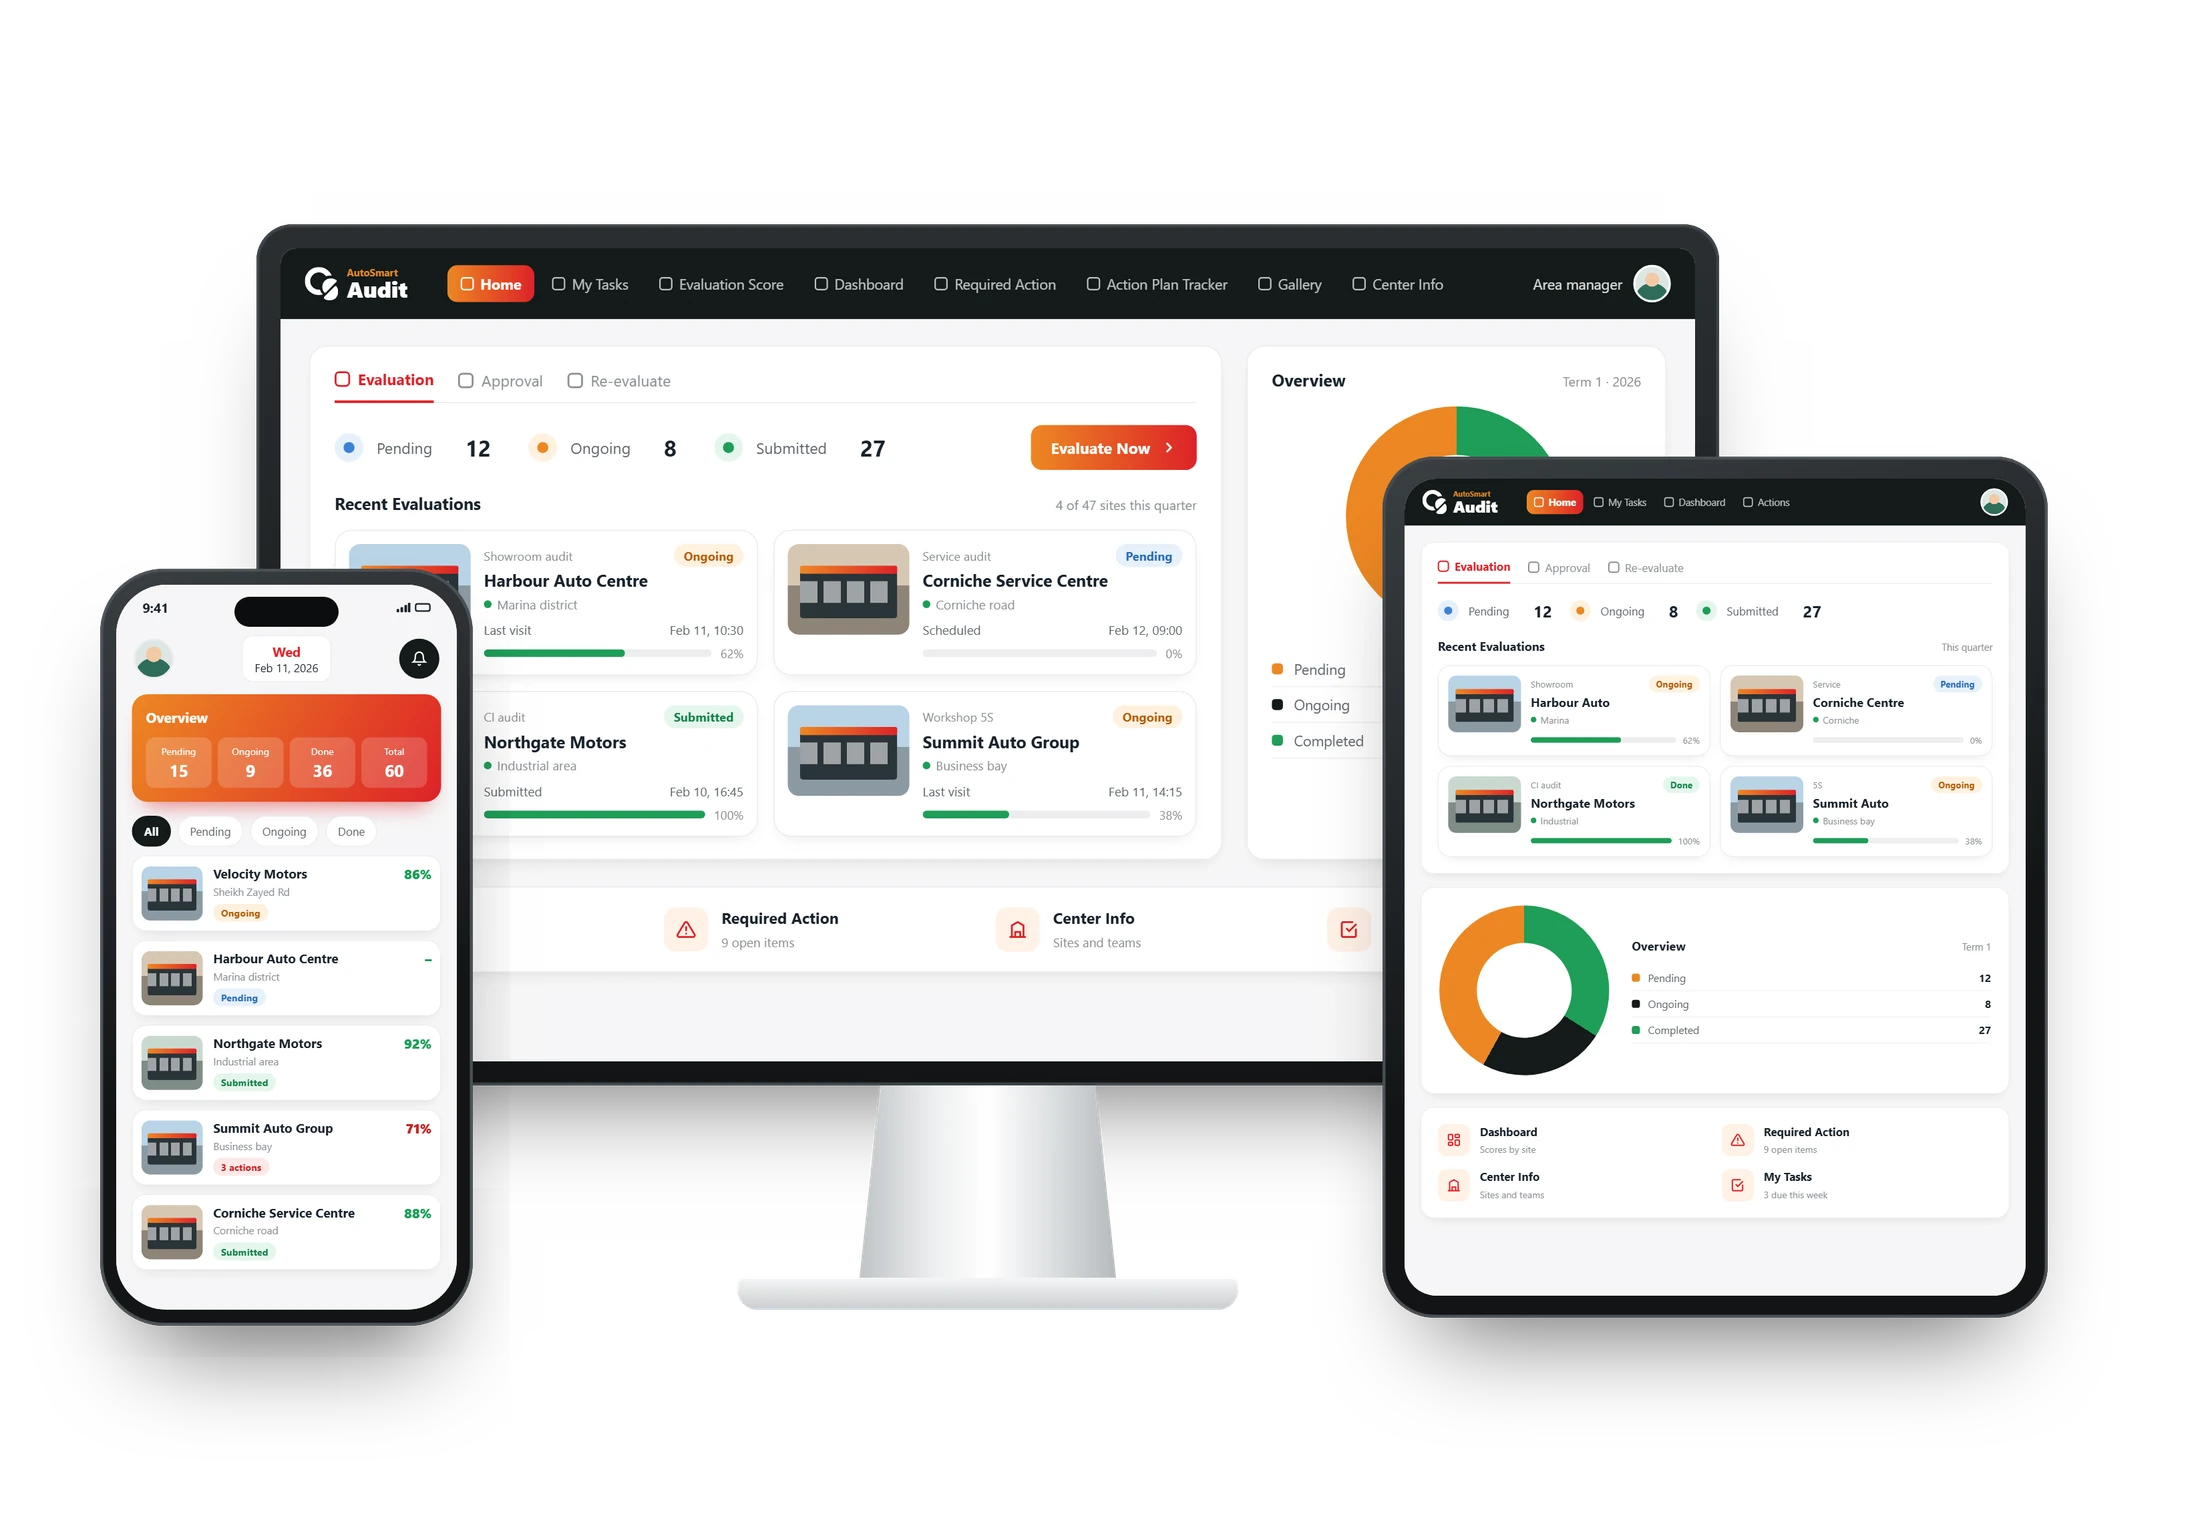
- Walk the site, standard by standard. Score each of the 12 checkpoints Pass, Fail or N/A. N/A only where the standard rules it out, with the reason recorded. Check consent forms and test an opt-out, collect the clauses from every channel, walk the showroom to see where customer files are kept, and check MFA on the DMS and CRM.
- Capture the evidence. A pass counts only with proof captured at the time of the audit: consent forms and opt-out test results, information clauses, the requests register, photos and system settings, processing agreements and the deletion schedule.
- Give every fail an owner and a fix time. Record what you saw and who owns the fix. Each standard carries an ideal fix time, from immediate to 30 days, counted from audit submission (see the table above).
- Fix it, then prove it. The site fixes the cause and uploads proof of closure; the auditor checks the proof before closing the finding.
- Re-check at the next audit. Confirm closed findings stay closed, and look for the same fail at your other sites so one gap doesn't repeat across the network.
Who this guidebook is for
- Boards: the size of the risk
- Marketing and sales: collecting consent correctly
- Data protection officers (IOD) and auditors: testing consent and requests
A reference document, not legal advice. Fines and rules change: check the current text with the regulator or your legal adviser before acting.